If you are planning to start a career in cybersecurity, the CompTIA Security+ (SY0-701) certification is usually the first serious step. It is one of the most recognized entry-level security certifications in the world, and it opens the door to roles like SOC analyst, IT security specialist, and network administrator.
This guide walks you through everything you need to know about the SY0-701 exam, the domains it covers, how to study for it, and how to pass it without wasting months on the wrong material.
What Is CompTIA Security+ (SY0-701)?
CompTIA Security+ SY0-701 is the current and only active version of the Security+ certification exam, and it has been the standard since late 2023. It replaced the older SY0-601 version, reducing the number of objectives while placing greater emphasis on practical, real-world security operations rather than pure theory.
In simple words, CompTIA Security+ SY0-701 tests what you can actually do, not just what you can memorize.
Quick Exam Facts
| Detail | Information |
| Exam Code | SY0-701 |
| Number of Questions | Up to 90 |
| Time Limit | 90 minutes |
| Passing Score | 750 out of 900 |
| Question Types | Multiple-choice and Performance-Based Questions (PBQs) |
| Certification Validity | 3 years |
Why This Matters for Your Study Plan
Knowing the format before you start studying stops you from over-preparing for question types that barely appear on the exam, and under-preparing for the performance-based questions that trip up most first-time candidates.
SY0-701 Exam Domains (Full Breakdown)
The exam is divided into five domains, and each one carries a different weight. Knowing these weights is the single most important thing before you start studying, because it tells you where to spend most of your time.
| # | Domain | Weight |
| 1 | General Security Concepts | 12% |
| 2 | Threats, Vulnerabilities, and Mitigations | 22% |
| 3 | Security Architecture | 18% |
| 4 | Security Operations | 28% |
| 5 | Security Program Management and Oversight | 20% |
Domain 1: General Security Concepts (12%)
This domain builds your foundation. It covers basic security controls, the CIA triad (Confidentiality, Integrity, Availability), cryptographic concepts, and fundamental terminology used throughout the rest of the exam.
Key Topics in This Domain
- CIA triad and core security principles
- Types of security controls (technical, managerial, physical)
- Basic cryptographic concepts and use cases
- Change management and security implications
Domain 2: Threats, Vulnerabilities, and Mitigations (22%)
Here you learn to identify attack types, malware, social engineering tactics, and the vulnerabilities attackers exploit — along with the mitigation techniques used to stop them.
Key Topics in This Domain
- Social engineering techniques (phishing, pretexting, vishing)
- Malware types (ransomware, trojans, worms, spyware)
- Common vulnerability types and attack vectors
- Indicators of compromise and mitigation techniques
Domain 3: Security Architecture (18%)
This domain focuses on secure network and system design, including cloud security, zero trust concepts, and how to architect infrastructure with security built in from the start.
Key Topics in This Domain
- Zero trust architecture principles
- Cloud, hybrid, and on-premises security design
- Data protection and data classification strategies
- Resilience and recovery concepts (backups, redundancy)
Domain 4: Security Operations (28% — The Largest Domain)
This is where the exam puts most of its weight. It covers day-to-day operational tasks: incident response, monitoring, identity and access management, and the tools security teams use in a real SOC environment.
Key Topics in This Domain
- Incident response process and procedures
- Identity and access management (IAM)
- Security monitoring tools (SIEM, EDR/XDR, SOAR)
- Vulnerability management and patching
Domain 5: Security Program Management and Oversight (20%)
Formerly known as “Governance, Risk, and Compliance,” this domain covers risk management, compliance frameworks, security policies, and third-party/vendor risk.
Key Topics in This Domain
- Risk management processes and terminology
- Compliance frameworks and regulatory requirements
- Security policies, standards, and procedures
- Third-party and vendor risk management
How to Create a Study Plan for SY0-701
A study plan works best when it’s built around domain weight, not gut feeling. Here’s a simple framework you can follow:
- Start with the official objectives document
- CompTIA publishes a free PDF listing every testable topic. Nothing outside this list appears on the exam.
- Allocate study time by weight.
- Spend the most hours on Security Operations (28%) and Threats/Vulnerabilities (22%), since together they make up half the exam.
- Use one primary study source.
- Pick a single book, video course, or platform as your main resource instead of jumping between many.
- Practice with performance-based questions (PBQs)
- These simulate real tasks and are often where candidates lose the most points if unprepared.
- Take full-length practice tests
- Simulate the 90-minute, 90-question format at least twice before exam day.
- Review weak domains in the final week.
- Don’t restart everything; focus only on the topics where your practice scores are lowest.
Suggested Weekly Time Split (Example)
| Domain | Weekly Study Time |
| Security Operations | 6–8 hours |
| Threats, Vulnerabilities, and Mitigations | 5–6 hours |
| Security Program Management | 4–5 hours |
| Security Architecture | 4 hours |
| General Security Concepts | 2–3 hours |
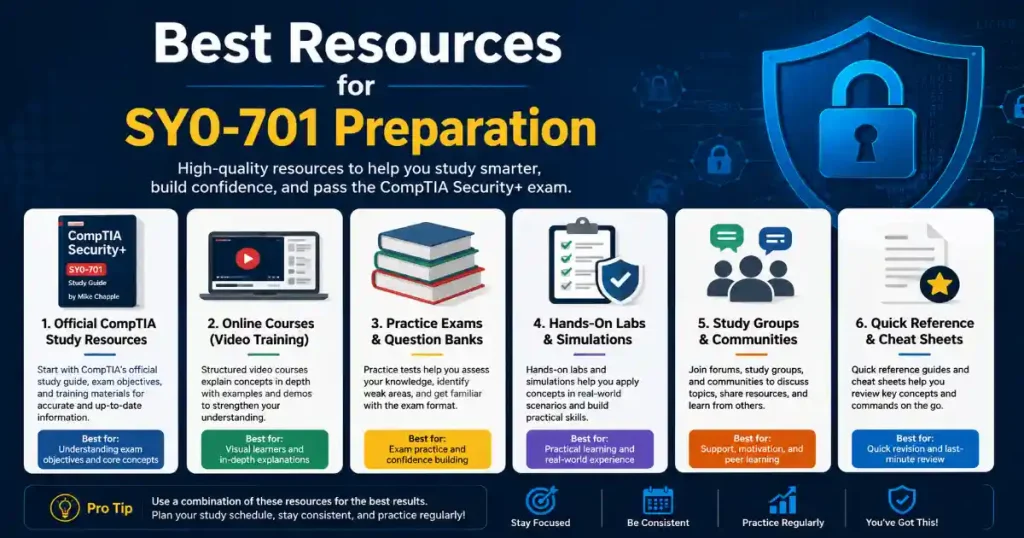
Best Resources for SY0-701 Preparation
- Official CompTIA Study Materials: CertMaster Learn and the official exam objectives PDF
- Video Courses: structured lessons that explain concepts with real examples
- Practice Question Bank: hundreds of sample questions mapped to each domain
- Hands-on Labs: useful for understanding PBQs, especially for networking and firewall configuration tasks
- Study Groups/Forums helpful for clearing doubts and staying motivated
Common Mistakes Beginners Make
- Studying SY0-601 material by mistake always confirm your resource is updated for SY0-701.
- Ignoring Security Operations because it “feels” less interesting, despite it being 28% of the exam
- Skipping practice tests until the last week instead of starting them early
- Memorizing definitions without understanding how concepts apply in real scenarios
Why CompTIA Security+ Still Matters in 2026
Security+ remains a DoD 8570/8140-approved certification, making it valuable for both private-sector and government- or defense-related IT roles. It’s vendor-neutral, meaning the skills apply across different tools and platforms rather than locking you into one ecosystem a major reason employers still list it as a baseline requirement for entry-level security positions.
Conclusion
The CompTIA Security+ SY0-701 exam rewards candidates who study smart, not just hard. Understanding the domain weights, focusing extra time on Security Operations and Threats/Vulnerabilities, and practicing with performance-based questions will put you in a strong position to pass on your first attempt. Use the official objectives as your checklist, stick to one primary resource, and test yourself regularly; that combination is what actually gets people certified.
(FAQs)
1. Is SY0-701 the current version of CompTIA Security+?
Yes, SY0-701 is the current and only active version of Security+. It has been active since November 2023 and replaced SY0-601, which is now retired.
2. How long does it take to prepare for CompTIA Security+ SY0-701?
Most beginners need about 2–3 months of consistent study. The exact time depends on prior IT knowledge and how many hours per week you can dedicate to studying.
3. What is the passing score for SY0-701?
The passing score for SY0-701 is 750 out of 900.
4. Do I need any prior experience before attempting Security+?
No formal prerequisite is required for Security+. However, CompTIA recommends having basic networking and systems administration knowledge, such as through Network+, before attempting the exam.
5. How long is the CompTIA Security+ certification valid?
The CompTIA Security+ certification is valid for 3 years. After that, it must be renewed through continuing education units (CEUs) or by retaking the exam.
